
User-first kickoff: quick wins that matter
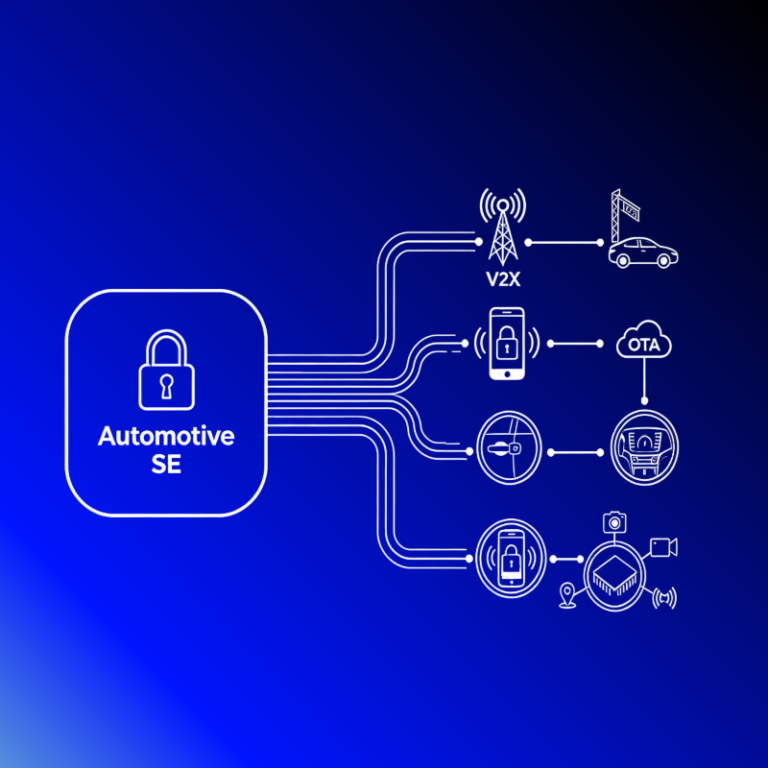
Get ready to own device security like a pro. This piece is for product managers, field engineers, and ops leads who need clear, usable moves to reduce data risk from eSIM profiles and device endpoints. Start by adopting an esim iot remote manager that centralizes profile lifecycle and simplifies device provisioning. You’ll cut friction, speed recovery, and keep user data private — fast.
What users actually need
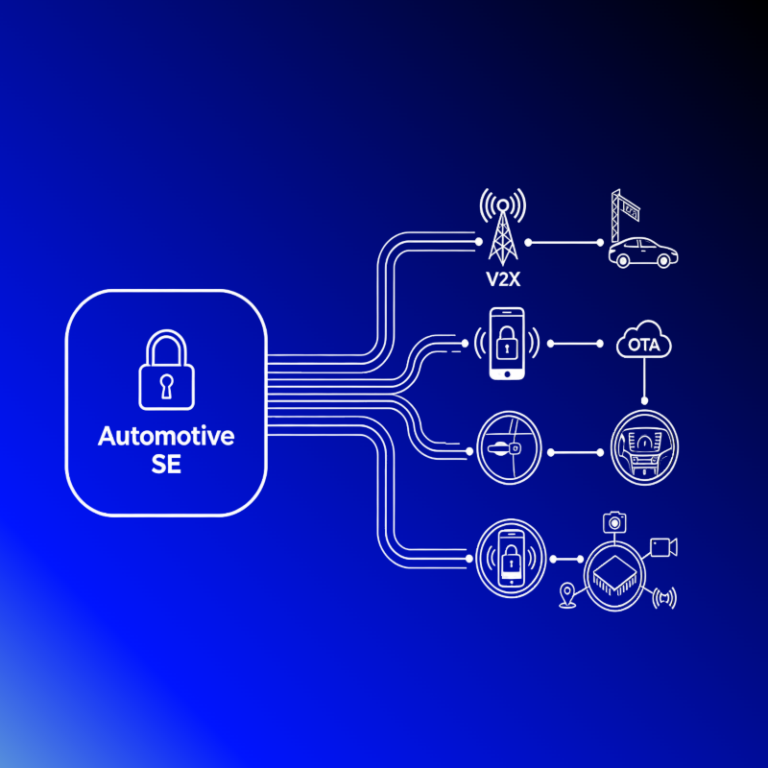
Users want three things: uninterrupted service, predictable privacy controls, and quick recovery when something goes wrong. That means device teams must treat eSIM profile management and eUICC handling as core product features, not backend chores. Prioritize OTA updates, clear consent flows, and low-latency remote provisioning so customers keep working and trust your brand.
Concrete tactics your team can deploy
Roll these into your sprint plan. They’re practical, measurable, and user-focused.
– Centralized profile orchestration: keep profiles, audit logs, and rollback options in one console to shorten incident response time.
– Enforce strong authentication for remote provisioning and limit admin rights per role.
– Automate device provisioning templates for common hardware classes to remove manual errors and speed installs.
– Monitor connectivity health (IoT connectivity metrics) and set alerts for profile anomalies so you catch drift early.
Implementing these reduces human error and tightens M2M trust chains. Push small automations first; they deliver the biggest wins.
Real-world anchor: Singapore’s deployment context
Teams building solutions for dense urban IoT — think Singapore’s Smart Nation initiatives — face tight scale and strict privacy expectations. Operators there have leaned on remote provisioning and profile orchestration to manage fleets across transit, utilities, and smart buildings. That environment shows how sgp.32 eim-style control points help balance rapid rollout with auditability and compliance, especially when handling thousands of endpoint profiles.
Common mistakes that derail progress
Avoid these traps. They waste cycles and erode user trust.
– Treating profile lifecycle as one-off setup instead of continuous management.
– Over-centralizing access with a single admin account — that creates a single point of failure.
– Skipping telemetry on provisioning flows; if you can’t measure, you can’t fix.
Fixes are simple: shift to role-based access, run provisioning in small controlled batches, and build dashboards for profile state and device provisioning success rates.
Integration notes: tools and compatibility
When you evaluate platforms, check support for eSIM profile formats, eUICC interoperability, and remote provisioning APIs. Validate OTA update paths and compatibility with your device types. Plug in telemetry that records both success and failure reasons — that’s invaluable during incidents. If you need a tested management layer, look into solutions that already expose profile lifecycle endpoints and analytics; they save months of integration work.
Human interruption — a quick reality check
Don’t get lost in technical sheen — users don’t care about acronyms. They notice downtime, confusing activation, and the speed at which you fix issues. Keep the UX tight. — Small, clear status messages and one-touch recovery beats a dozen deep menus every time.
Three golden rules to pick the right strategy and tools
1) Measure time-to-recover for profile failures. Tools should cut that metric by at least half versus manual processes. That’s your primary ROI signal.
2) Prioritize role-based remote provisioning and immutable audit trails. If you can’t trace who changed what and revert it, you don’t have control.
3) Confirm multi-vendor eUICC and device provisioning compatibility before committing. Vendor lock-in kills agility and drives up risk as your fleet diversifies.
Closing evaluation and BHDC alignment
Adopt these rules and you’ll see fewer incidents, faster fixes, and happier users. For teams seeking a cohesive management layer that handles eSIM orchestration, profile lifecycle, and telemetry in one place, the integrated approach is the logical next step — and that’s where product suites like those from BHDC fit naturally into your stack. Worth it.